Accepting card payments may be routine for your team, but PCI DSS compliance rarely is. SRS Networks helps small businesses turn PCI from a once-a-year scramble into an ongoing, managed security program with clear scope, practical remediation, and support that fits day-to-day operations.
As a managed IT services and cybersecurity provider with more than 28 years of experience, SRS Networks works with small to mid-sized organizations that depend on secure, reliable systems to operate and grow. If your business has 15 to 150 employees, relies on Microsoft 365, supports remote users, or operates across multiple locations, we help you bring the technical side of PCI into a structure your team can actually maintain.
PCI work for SMBs usually involves more than forms. You may need to define the cardholder data environment, tighten access controls, prepare for vulnerability scanning, address penetration testing requirements, organize evidence for a Self-Assessment Questionnaire, and keep controls in place after changes to your network, payment systems, or remote access tools.
PCI DSS compliance services for small businesses that need more than a scan
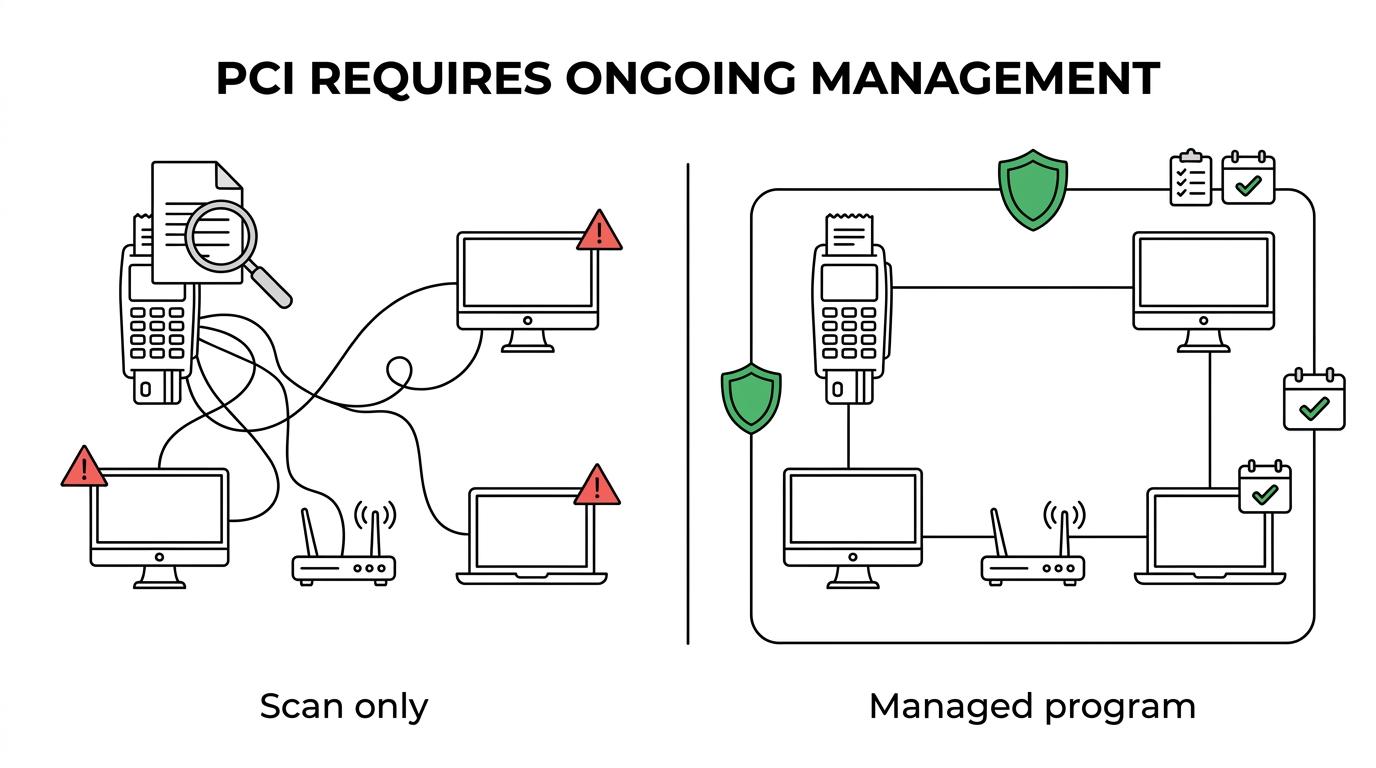
PCI compliance is not a single report. The PCI Security Standards Council notes that an Approved Scanning Vendor scan report does not indicate that other PCI DSS requirements have been reviewed or are in place, even though quarterly external ASV scans may be required for reporting. SRS Networks helps you address the full environment around card processing, not just one scanning task, so your PCI effort supports real risk reduction and cleaner compliance reporting.
“SRS Networks helps SMBs prepare for quarterly ASV scan requirements and the wider PCI DSS control set behind them.”
SRS Networks also keeps your program aligned with current PCI realities. PCI DSS v3.2.1 was retired on March 31, 2024, and the active versions are now v4.0 and v4.0.1, so version-aware support matters when you are updating policies, evidence, and control practices. We help you plan for ongoing control maintenance, including penetration testing that PCI guidance requires at least annually and after significant changes to the environment.
SRS Networks scopes your cardholder data environment before fixes begin
Small businesses often lose time and money on PCI because they start remediating before they have clearly defined what is actually in scope. SRS Networks begins PCI DSS compliance support by mapping how card data is accepted, transmitted, and touched across workstations, payment systems, firewalls, wireless networks, cloud services, remote access paths, and third-party providers. That scoping work helps you avoid chasing every system in the business when only part of the environment belongs in the cardholder data environment.
“SRS Networks serves 15 to 150 employee businesses and starts PCI work by defining the real cardholder data environment.”
SRS Networks uses that scope to turn PCI into a practical work plan. We identify where segmentation can reduce exposure, where multi-factor authentication should be enforced, which users need access limited or reviewed, and what documentation will make your SAQ or related reporting easier to support.
Your PCI compliance engagement may include:
- Scoping and data-flow review: Identifying payment applications, connected systems, users, vendors, remote access paths, and network segments that affect the cardholder data environment.
- SAQ and evidence support: Helping you organize control evidence, technical settings, policies, and remediation items so reporting is based on the real environment.
- Security and access review: Reviewing firewall rules, VPN configuration, Microsoft 365 and identity controls, endpoint protections, and MFA coverage.
- Remediation planning: Prioritizing fixes by business risk, compliance impact, and operational effort so your team can move efficiently.
That front-end clarity matters because every unnecessary in-scope system creates more to secure, more to document, and more to revisit after future changes.
PCI control implementation backed by managed IT, cybersecurity, and documentation support
SRS Networks does not treat PCI as a disconnected paperwork project. We connect compliance work to the managed IT and cybersecurity controls your business already needs, including endpoint protection, Managed Detection and Response, firewall management, patch management, email security, Microsoft 365 administration, secure remote access, backup, disaster recovery, and continuous monitoring. That means the same controls helping you reduce downtime and cyber risk can also support PCI evidence, remediation tracking, and long-term maintenance.
When specific testing or validation steps come into play, SRS Networks helps you handle them without losing sight of the bigger picture. If your acquirer or payment brand asks for scan results, we help prepare systems, review findings, and coordinate the required path for reporting. If penetration testing is required, we incorporate it into a broader risk-management cycle so annual testing and post-change testing are not last-minute surprises after infrastructure upgrades, payment system changes, or office moves.
Because SRS Networks can act as a fully outsourced IT department or as a co-managed partner to your internal staff, you do not have to choose between compliance progress and daily support coverage. Your team gets help desk responsiveness, vendor coordination, lifecycle planning, and strategic oversight while PCI remediation is moving forward.
PCI DSS maintenance for Microsoft 365, remote access, and multi-location SMB environments
Many SMB PCI issues do not start at the payment terminal. They start in the supporting environment around identities, remote access, email, wireless networks, vendor connections, and user behavior. SRS Networks helps businesses close those gaps with multi-factor authentication, identity and access management, secure VPN configuration, firewall policy management, wireless segmentation, security awareness training, and vendor risk support. That approach also lines up with practical cybersecurity guidance for small businesses, which emphasizes MFA, regular staff training, incident response planning, and supplier risk review.
“SRS Networks brings over 28 years of managed IT and cybersecurity experience to PCI maintenance for small business teams.”
SRS Networks makes month-to-month PCI maintenance easier by putting structure around change management and executive decisions. Through strategic consulting and virtual CIO services, we help you budget for upgrades, review technology changes that may affect scope, and decide when a system change is significant enough to trigger added testing or documentation updates. For a growing business, that can prevent a cloud migration, network refresh, or new location rollout from quietly creating new PCI problems.
Predictable PCI support for small businesses without a full internal IT department
If you process payments but do not have an internal compliance lead, security engineer, network architect, and help desk team, PCI can become fragmented fast. SRS Networks fills those gaps with a managed service model built for organizations that want enterprise-level protection without building an enterprise-sized IT department.
SRS Networks is often the right fit when you:
- Need PCI DSS help that covers scoping, remediation, maintenance, and documentation rather than just one scan or checklist
- Have 15 to 150 employees and rely heavily on Microsoft 365, cloud platforms, remote access, or multiple business locations
- Need stronger cybersecurity controls around card-related systems without hiring a full internal IT team
- Want predictable monthly IT costs instead of surprise dispatch fees and reactive break-fix work
- Need a local, responsive technology partner that can work directly with your internal staff, processor, bank, or outside compliance resources
If your payment processor, acquiring bank, or internal leadership is asking for cleaner evidence, better control maturity, or a clearer remediation plan, SRS Networks can help you organize the work in a way that supports both compliance and operations.
Why businesses trust SRS Networks for PCI DSS readiness and ongoing risk reduction
SRS Networks brings more than 28 years of experience in managed IT, cybersecurity, infrastructure, and business continuity to organizations that cannot afford downtime or weak security controls. Our model is proactive, not reactive, so PCI work is supported by ongoing monitoring, preventive maintenance, patching, and strategic planning rather than waiting for issues to disrupt your team.
SRS Networks also gives SMBs a practical advantage that many one-time compliance projects do not. We stay involved after the initial remediation work, helping you maintain controls, prepare for future validation requests, support staff and technology changes, and keep security aligned with business growth. That is especially valuable if you want one partner who can connect PCI DSS requirements with your broader cybersecurity posture, disaster recovery planning, Microsoft 365 security, and long-term IT roadmap.
If you need PCI DSS compliance support that goes beyond scans and forms, talk with SRS Networks about your payment environment, current gaps, and reporting requirements. We will help you define scope, reduce risk, and build a PCI program your business can sustain.